Latest updateInvestigating01:33 UTC ()
p95 latency on the public API is above 500 ms. Requests are completing, more slowly than usual.
- Identified01:59
A slow query on the usage endpoint is holding connections. The fix is rolling out now.
ProductCustomer pages
One page behind your app's sign-in. Each customer sees the same services, measured against the targets in their contract, with the incidents that concern them.
Latest updateInvestigating01:33 UTC ()
p95 latency on the public API is above 500 ms. Requests are completing, more slowly than usual.
A slow query on the usage endpoint is holding connections. The fix is rolling out now.
Latest updateIdentified02:02 UTC ()
Your dedicated export worker is behind. Exports finish, up to 15 minutes late.
At a glance
Uptime, 30 days
99.57%Services operational
3of 4Active incidents
2API availability
API
API latency under 500 ms
API
Dashboard availability
Dashboard
Webhook deliveries are running up to ten minutes late.
Workers are back to full capacity. Watching the queue drain.
The queue has drained and every delayed event was delivered.
Targets
Override a target for one customer. The same readings are measured against it, so a stricter contract shows its own error budget.
Signed in as Globex
The standard 99.90% target.
API latency under 500 ms
API
API availability
API
Signed in as Northwind
Their contract says 99.95%.
API availability
API
API latency under 500 ms
API
Override
Both pages read the same 30 days: 99.94% available. Against 99.95% that is an exhausted budget, recomputed every five minutes. Every other customer keeps the default.
Contract
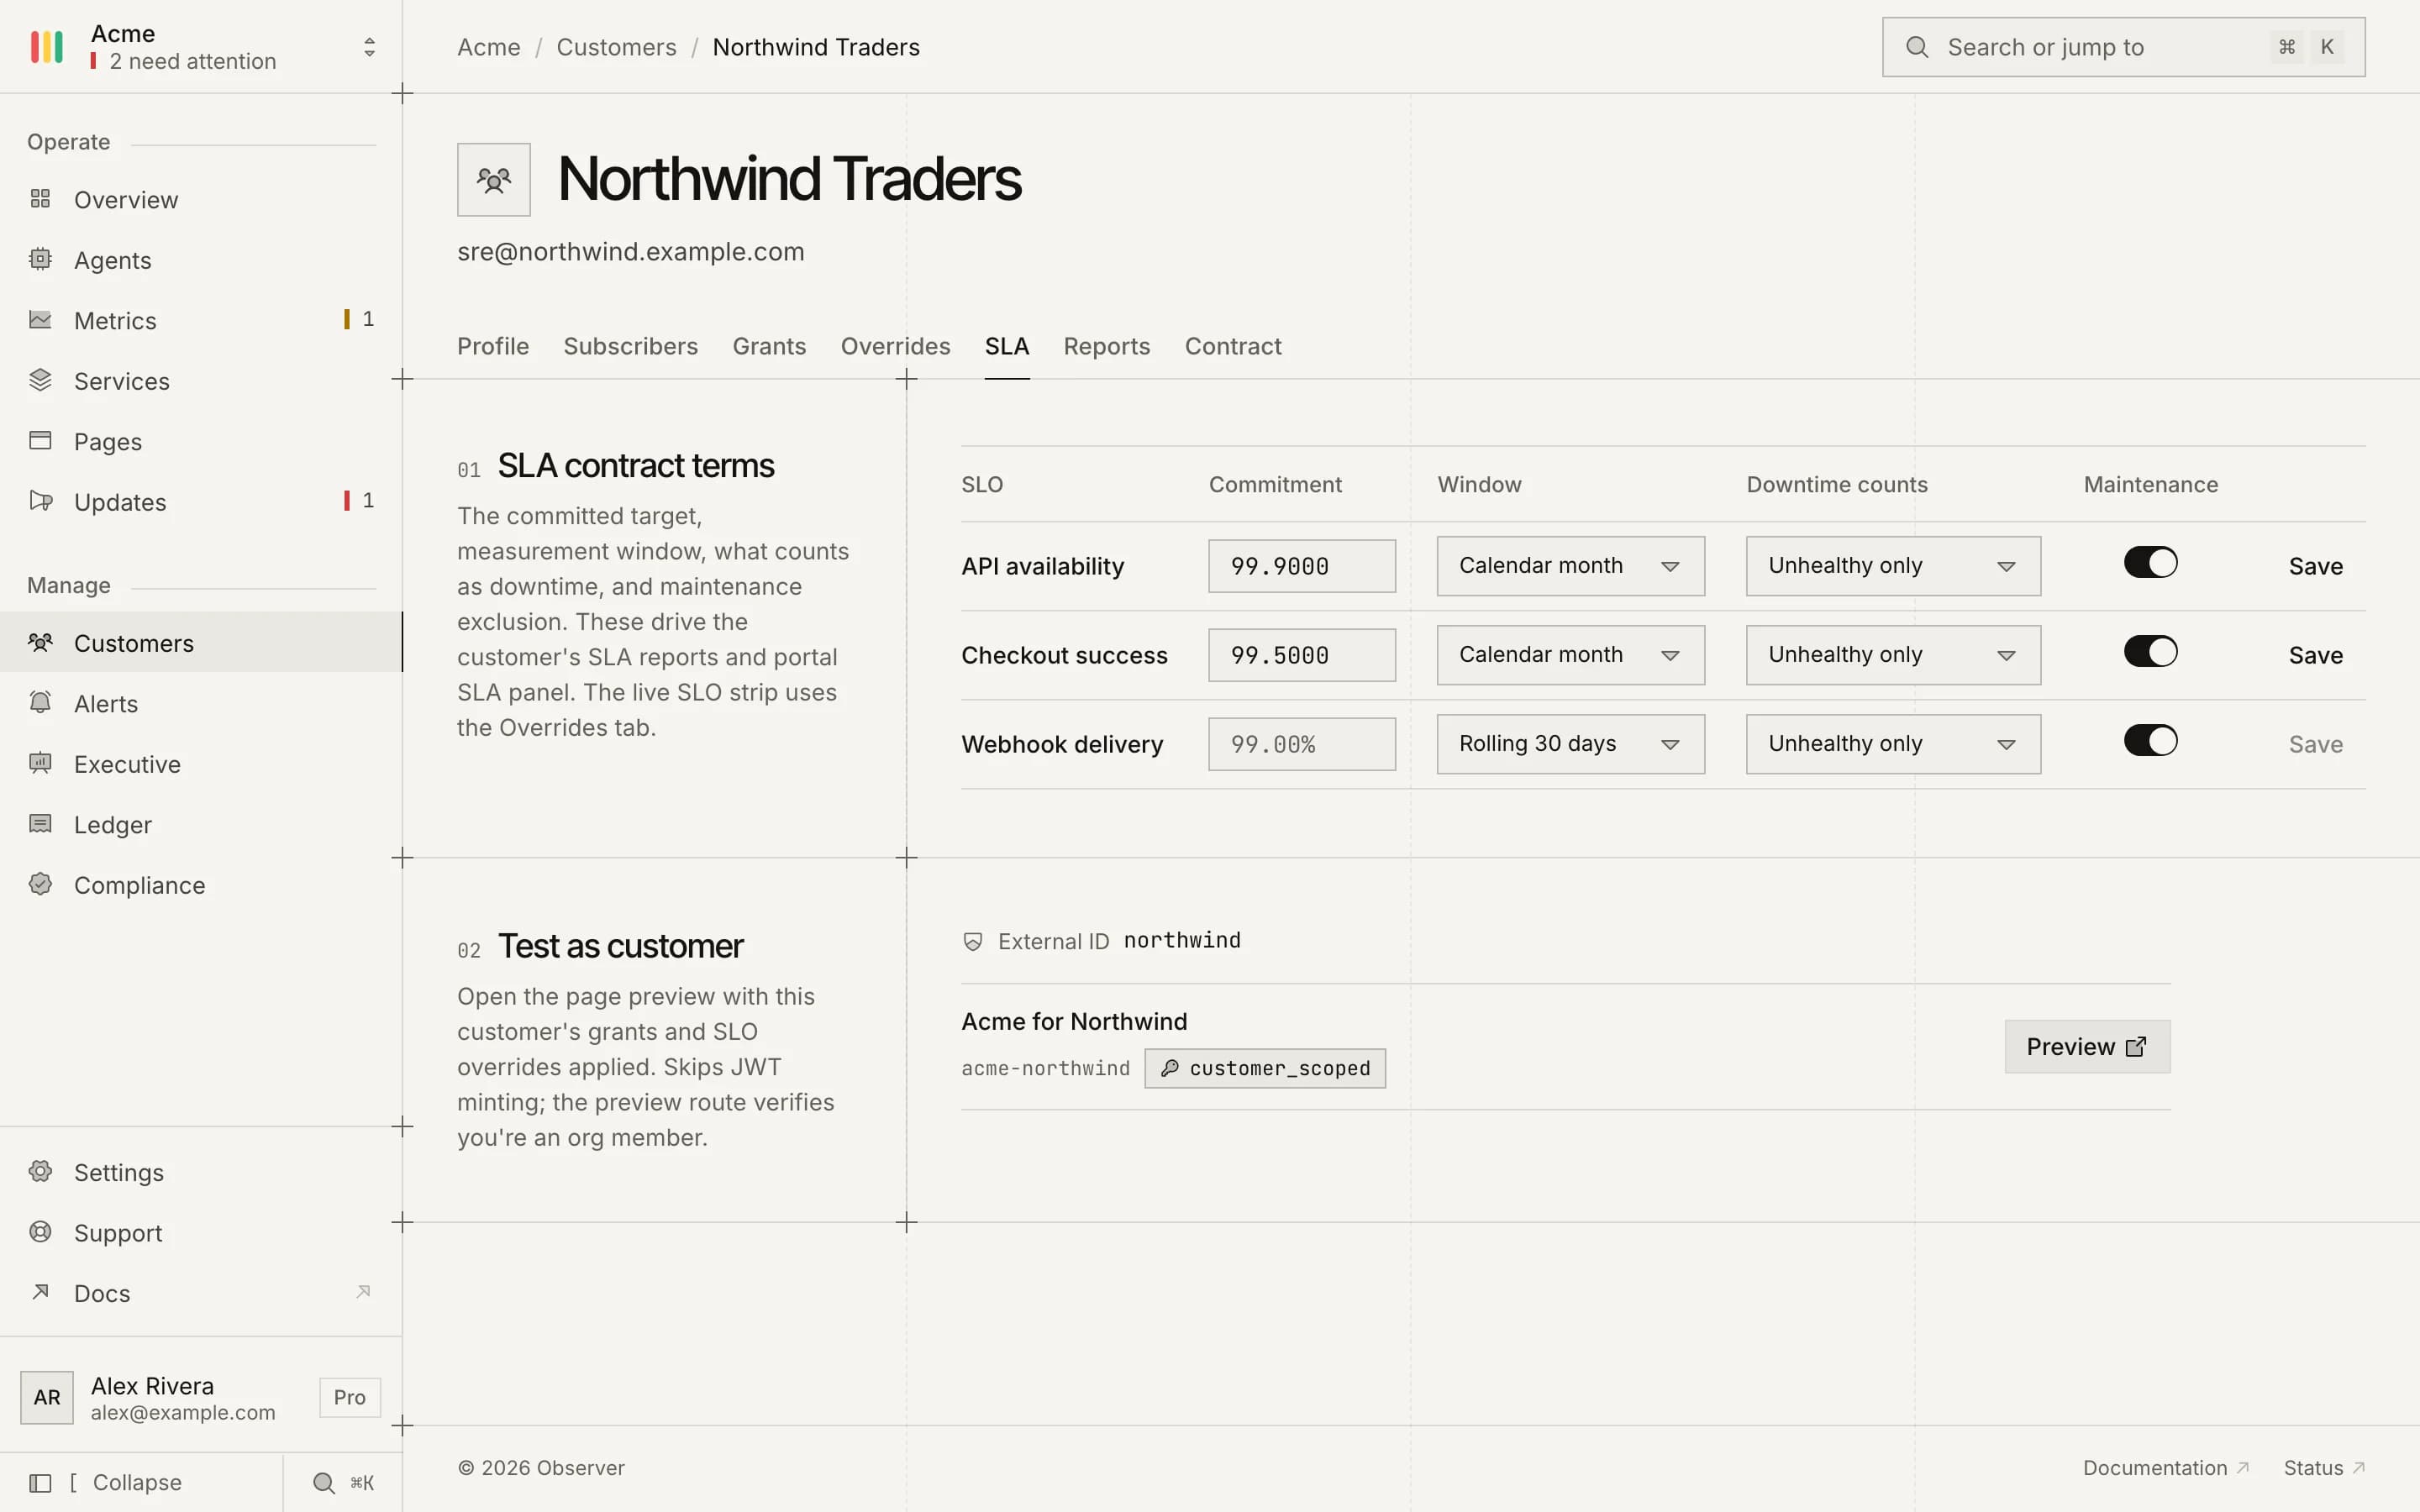
Record the terms you signed: the target, a rolling 30 days or a calendar month or quarter, whether degraded time counts as down, and whether planned maintenance is excluded. Their page shows the attainment for the period.
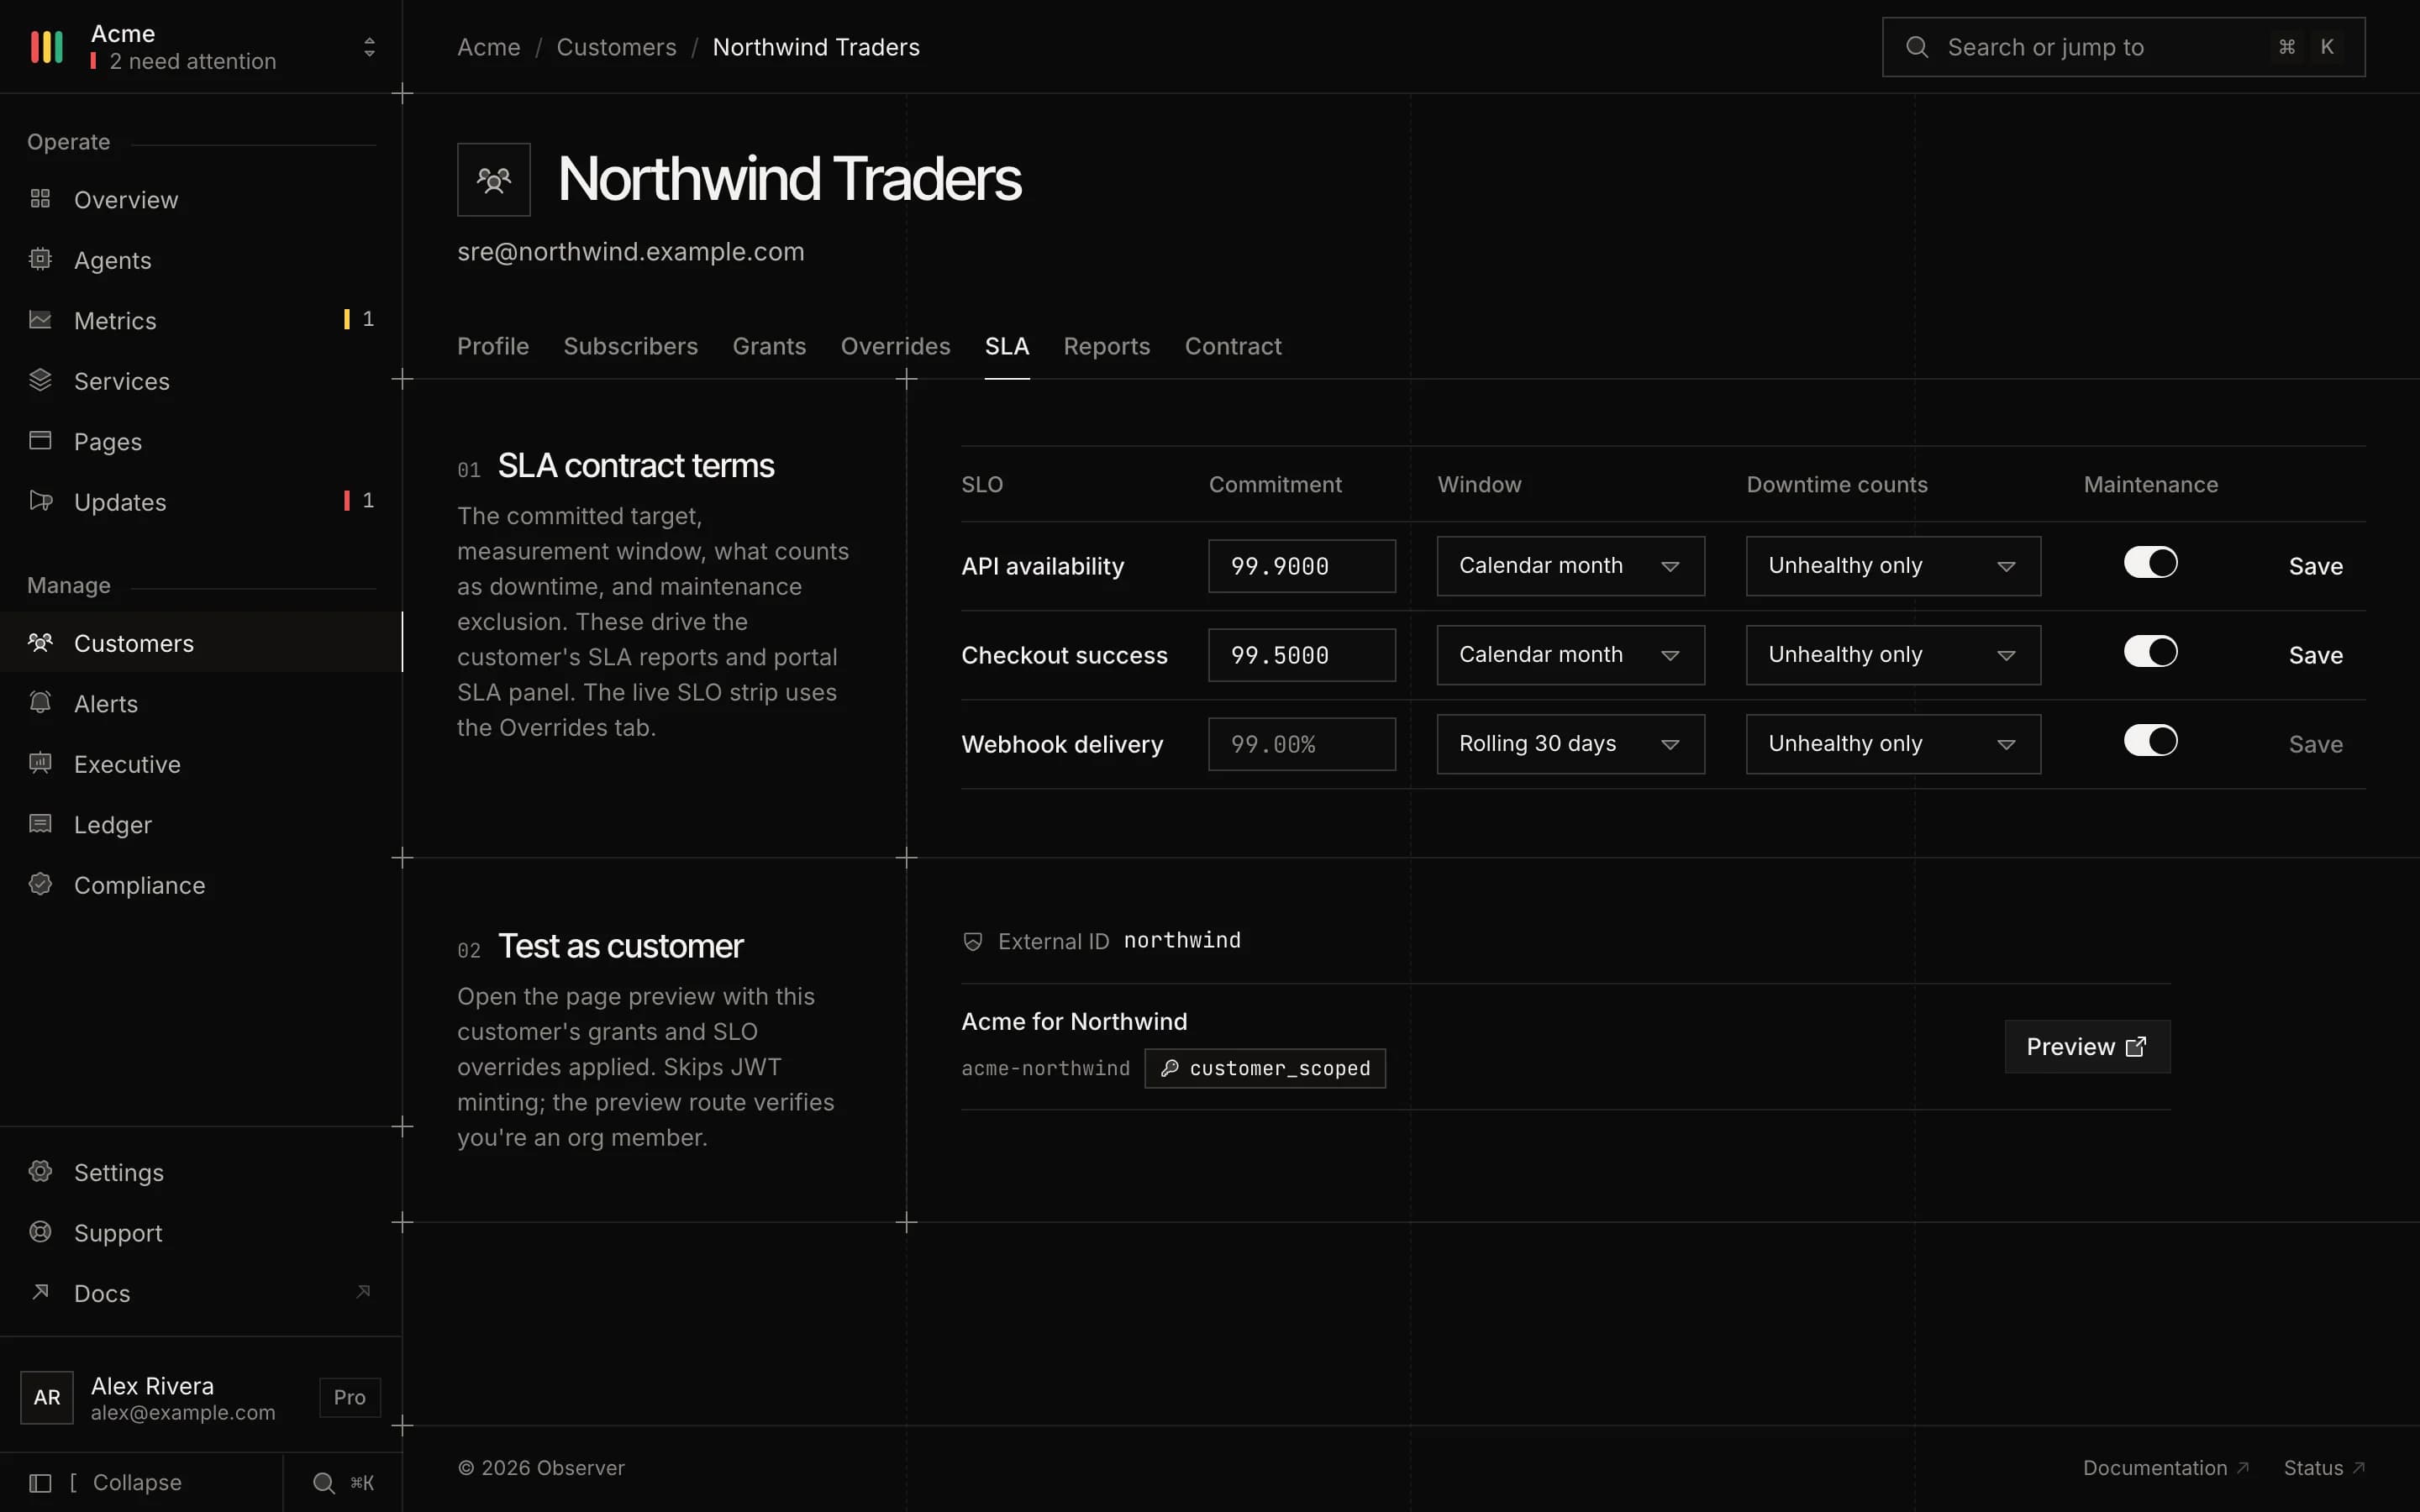
A customer's SLA terms in the console: target, window, what counts as down and the maintenance exclusion, per SLO.
Incidents
Mark who an incident affects. Keep it on the public page and email them too, or show it to them alone. Try the control from the incident form.
On the incident
Only Northwind can see this. Emails go to their linked subscribers on pages they have access to.
When you publish
| Audience | Sees it | Emailed |
|---|---|---|
| Public page[email protected] | No | No |
| Northwind[email protected] | Yes | Yes |
| Globex[email protected] | No | No |
| Initech[email protected] | No | No |
On a public incident, the resolve email also reaches anyone emailed earlier, even if you narrowed the list since.
Subscribers
Each subscriber can belong to a customer: from the page they signed in to, from your email rules, or by hand. Linked subscribers get that customer's private updates.
Email rules
A new subscriber
Linked to GlobexEmail rule
*.globex.io: globex.io and its subdomains. The most specific rule wins.
Signed link
A subscriber who signs up from a customer's page is linked to that customer. Rules never override it, and nothing is sent until they confirm by email.
Email rules
The most specific rule wins and a tie links nobody. Shared mailbox domains are refused: "gmail.com is a shared mail provider. Add exact addresses instead." Apply new rules to existing subscribers in one step.
By hand
A manual decision stays put. Rules and signed links never change it.
Access
Your customers never get an Observer account. Your app vouches for them with a signed token, and the page does the rest.
Customers
One at a time, or import up to 500 from a CSV with their email rules, page grants and target overrides.
Grant
A customer sees a page only once it has been granted to them. Grants and targets live on the customer.
Token
RS256, its subject the customer's ID, sent in a header or on the link. Observer checks it against your public key or JWKS URL, and refuses tokens older than an hour.
Preview
Open any customer's view from the console with their grants and targets applied, without minting a token.
Everyone else
The page checks the token before anything renders, and says why it refused.
Reliability
Give the page a Reliability Center and send each customer a private link to their part of it.
Access links
A link per customer and page opens their contract lines, attainment for the month so far and the statements delivered to them. Links expire after 90 days and can be revoked any time.
Plans
Customers per plan
Each with their own grants, targets, SLA terms and linked subscribers. Customer-scoped pages are capped at the same number.
Pro
0customers25 customer-scoped pagesBusiness
0customers100 customer-scoped pagesEnterprise
UnlimitedUnlimited customer-scoped pages